End-to-end encryption with government records and recovery in mind.
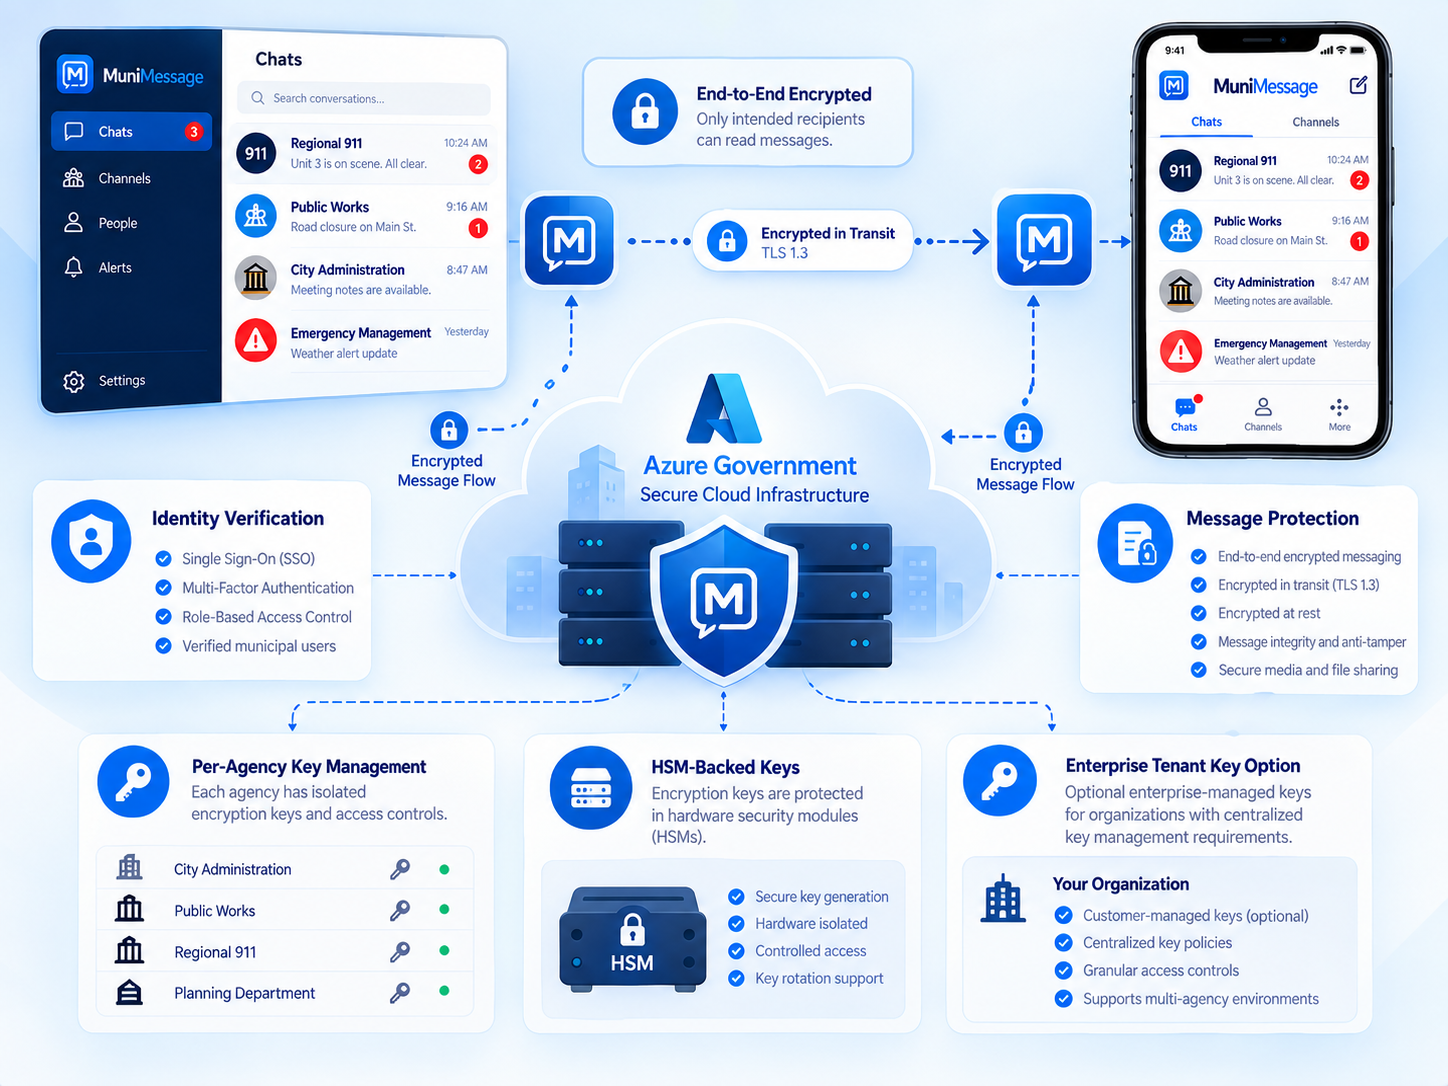
Messages are encrypted on user devices. Routine application services operate on encrypted content, while separately authorized, audited agency recovery supports government records obligations.
Azure Government
The CMI-operated messaging service runs in Microsoft Azure Government, with agency message content and retained records stored in the United States.
HSM-backed key protection
Tenant compliance and recovery key material is protected with hardware-backed cryptographic boundaries and tightly scoped recovery identities.
Per-agency isolation
Conversation and recovery key design keeps agency cryptographic boundaries separate rather than relying on one routine application master key.
Strong identity
Passkeys and modern authentication reduce reliance on reusable passwords and strengthen user authentication.
Controlled recovery
Authorized records recovery is separated from normal application access. Each recovery requires explicit authorization and a recorded reason, and creates an audit trail and notification to designated agency administrators.
Enterprise custody options
Enterprise deployment options can support customer-controlled key custody where requirements call for additional organizational control.
Security standards and agency requirements
MuniMessage’s security design is informed by the FBI CJIS Security Policy and NIST SP 800-53 and SP 800-171, with an emphasis on strong authentication, controlled access, auditing, and protection of communications.
Explore MuniMessage for your organization.
See how MuniMessage can bring secure, accountable messaging into your organization.